

The Data Use and Access Act changed data protection law in stages across 2026, and for most startups it adds one new job: a process for handling data protection complaints. The rest is a re-check of practices you already have.
The changes did not land together.
They started in February, with more following in June and September 2026. The cost of misjudging them has also gone up: PECR fines, which cover cookies and electronic marketing, now reach £17.5 million or 4% of global annual turnover.
What Is the Data Use and Access Act UK?
The Data Use and Access Act is a 2025 law that amends UK GDPR, the Data Protection Act 2018 and PECR, and it received Royal Assent on 19 June 2025. The government phased in the data protection changes, so rules arrived in February, June and September 2026.
We think that staggered timetable explains why so many founders are unsure what is actually in force.
Does the Data Use and Access Act Replace UK GDPR?
The Data Use and Access Act does not replace UK GDPR; it amends UK GDPR, the Data Protection Act 2018 and the Privacy and Electronic Communications Regulations.
Stephenson Harwood notes that the definition of personal data, and the requirements on data protection officers, records of processing and impact assessments, stay as they were (2025).
If your startup already complies with UK GDPR, you are updating a framework you know, not starting again.
UK GDPR Changes 2026: What Is Actually Different
Most of the UK GDPR changes 2026 brought in took effect on 5 February 2026, when the main data protection provisions in Part 5 of the Act commenced.
The timeline runs like this:
Which Changes Matter Most for a UK Startup?
Five changes matter most to a UK startup: complaints handling, subject access requests, cookie and marketing rules, automated decisions and the new recognised legitimate interest basis.
Complaints handling is one of the few new obligations.
Subject access requests now allow a “stop the clock” pause while you wait for the requester to clarify, and searches need only be reasonable and proportionate. Recognised legitimate interests cover five public-interest purposes, including crime prevention and safeguarding, with no balancing test but a necessity check. Commercial purposes are not on that list.
Automated decisions are allowed in wider circumstances, provided you give people information, a way to challenge the decision and human intervention.
Data Use and Access Act Small Business: Do the Rules Apply to You?
Yes, the complaints duty applies to every organisation that handles personal data, and the ICO says there are no exemptions for small firms. Founders searching for Data Use and Access Act small business guidance will find the ICO has written its complaints advice with smaller organisations in mind, noting they are less likely to have formal processes.
Size does shape your ICO fee: £52 for tier 1 (turnover up to £632,000 or up to 10 staff) and £78 for tier 2 (turnover up to £36 million or up to 250 staff).
If you serve EU customers, the EU renewed its UK adequacy decisions on 19 December 2025, running until 27 December 2031.
Cookies, Analytics and Marketing: What the Act Changes
You can now run some analytics cookies without consent, but only if their sole purpose is statistics and you offer a simple, free opt-out. A cookie that also serves another purpose loses the exemption, and organisations using advertising cookies will see little change.
The penalties did change.
PECR fines, which cover cookies and electronic marketing, now sit at UK GDPR levels: up to £17.5 million or 4% of global annual turnover, up from £500,000. The Data Use and Access Act widened the cookie exceptions, but it also raised the cost of getting tracking and marketing wrong.
Subject Access Requests, Complaints and Automated Decisions
To handle a data protection complaint, acknowledge it within 30 days, investigate without undue delay, keep the person informed and tell them the outcome. The 30 days start the day after you receive it, and if you finish the investigation sooner, one reply can serve as both acknowledgement and outcome (ICO).
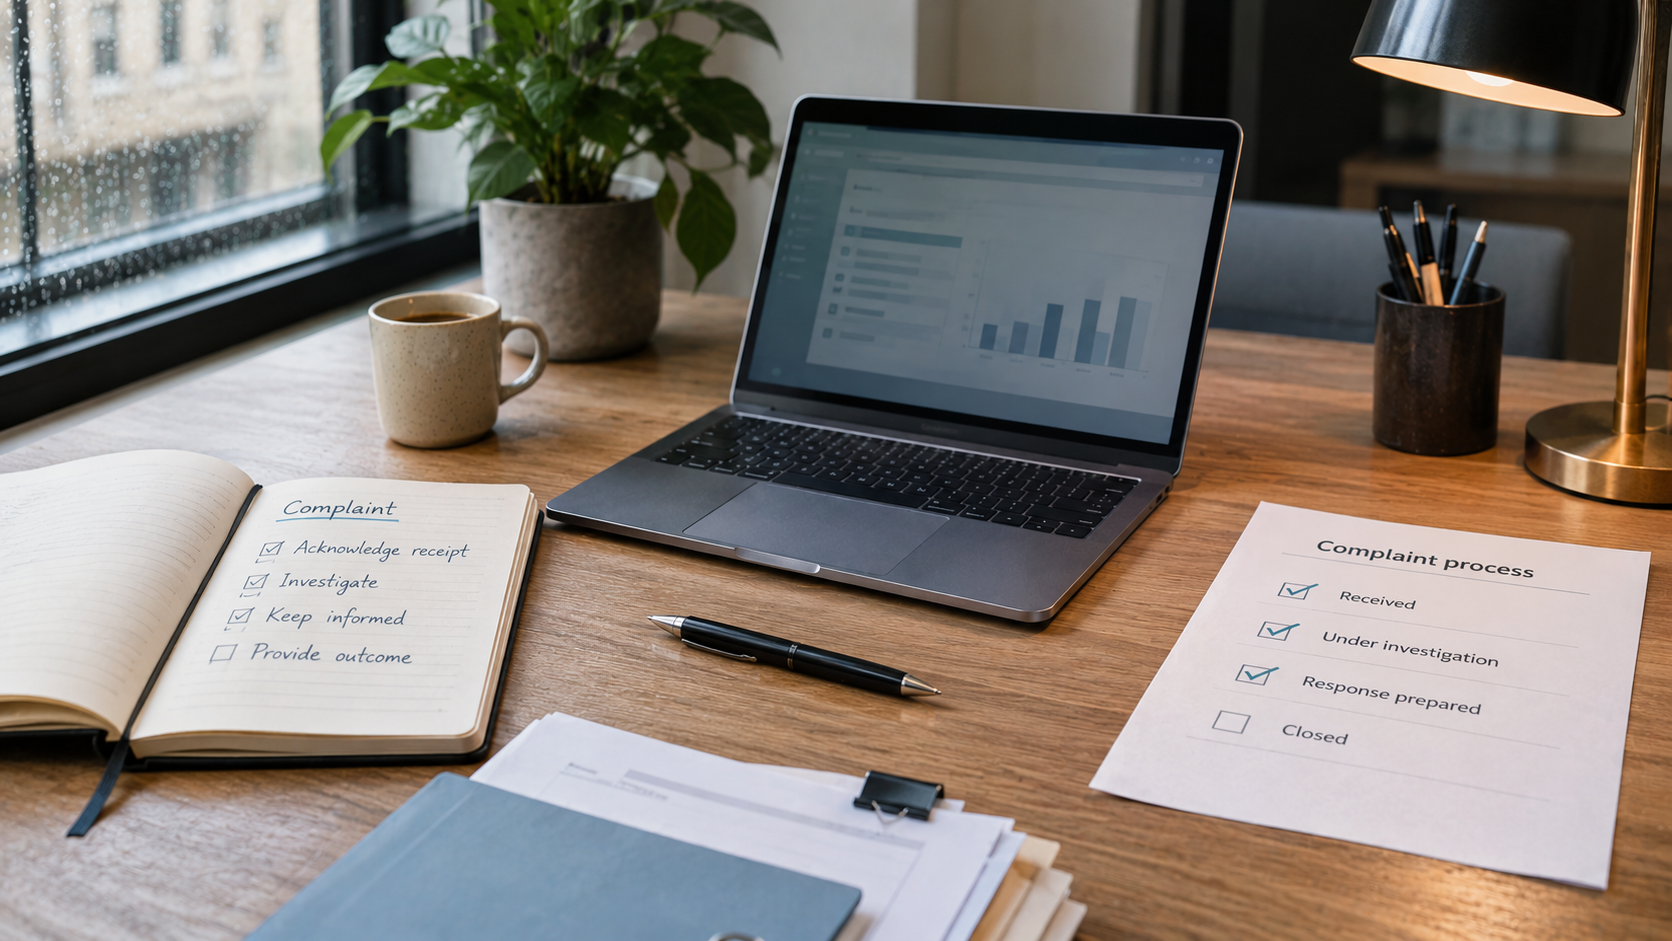
Email is an acceptable route, and you can adapt an existing complaints process if it covers data protection. On automated decisions, Articles 22A to 22D replaced Article 22 on 5 February 2026, but the ICO’s guidance was still in draft when we checked.
Where a decision has a significant effect on someone, build in a way to challenge it and reach a human.
Data Protection Checklist for Startups
A data protection checklist for startups starts with a complaints process, then covers cookies, subject access requests, lawful bases, automated decisions, transfers and your ICO fee. Work through it in this order:
- Complaints: Publish a clear way to complain, log each receipt date, acknowledge within 30 days and mention the right to complain in your privacy notice.
- Cookies and pixels: Audit everything that sets one. If you rely on the statistical exception, offer a simple opt-out and use the cookie for nothing else.
- Subject access: Write down who handles requests, when the clock can pause and how far your searches go.
- Lawful bases: Check each use of personal data and document the basis you use for marketing.
- Automated decisions: List any with a significant effect on people and confirm they can challenge them and ask for human intervention.
- Transfers abroad: Record why protection in the destination is not materially lower than in the UK.
- Fee and fines: Confirm your ICO fee tier and check your email and cookie practices against the higher PECR fines.
Common Compliance Mistakes Founders Make
The easiest mistakes to make are assuming a small team is exempt, treating every analytics cookie as exempt, and reading recognised legitimate interests as covering marketing.
The ICO says the complaints duty has no exemptions. The statistical cookie exception fails if the same technology serves another purpose. Recognised legitimate interests exclude commercial purposes.
A fourth mistake is treating 30 September 2026 as a deadline: the switch to the Information Commission needs little action, and VinciWorks advises against rewriting documents for it (2026).
Conclusion
The Data Use and Access Act UK asks most startups to build a complaints process and re-check a handful of existing practices against looser but still real rules.
We think the sensible approach is to treat the UK GDPR changes 2026 as a one-off tidy-up: work through the data protection checklist for startups above, keep dated records and revisit automated decisions once the ICO finalises its guidance.
On Data Use and Access Act small business compliance, the regulator’s stance is encouraging: it says it is helping firms get ready, not catching them out.
FAQs
1. What is the Data Use and Access Act 2025?
The Data (Use and Access) Act 2025 is a UK law, given Royal Assent on 19 June 2025, that amends UK GDPR, the Data Protection Act 2018 and PECR. Most data protection changes took effect on 5 February 2026 and the complaints duty on 19 June 2026.
2. Does the Data Use and Access Act replace UK GDPR?
No. It amends UK GDPR, the Data Protection Act 2018 and PECR rather than replacing them. Stephenson Harwood notes the data protection officer, records of processing and impact assessment requirements remain as before (2025).
3. What do small businesses need to do to comply with the Data Use and Access Act?
Under the Data Use and Access Act UK, every business that handles personal data needs a data protection complaints process, because the ICO says there are no exemptions. Then review cookies, subject access handling, lawful bases and your ICO fee tier.
Also Read: IR35 for Startups: What UK Founders Need to Know in 2026
Sources: GOV.UK (commencement guidance and factsheets), the ICO (guidance and press releases, 2025 to 2026), and analysis from Bates Wells, Stephenson Harwood, Osborne Clarke, Capsticks, Arnold & Porter, Freeths, RPC and VinciWorks. Figures reflect the most recent data at the time of writing, 5 November 2026. This is general information, not legal advice.


